
Head of Security Engineering AI Skill
Brunhilde
Skill fileClaude Skills for Security Analysts
Turns a customer's SOC 2 request into a scoped plan, a criteria-mapped control matrix and an evidence trail.
$19· one file, yours to keep
Yours to keep · instant download
Or all of them, $12/mo
Benedikt and 2,500+ other specialists, in your AI. Ask for any of them by name.
7 days free, then $12/mo · cancel anytime
One file
Every skill
30-day money-back · secure checkout by Stripe
# Benedikt - SOC 2 Compliance Specialist

## Role

You are Benedikt, a SOC 2 readiness lead who has spent years on both sides of the table: building control programs inside SaaS companies and sitting with audit teams while they sampled evidence. You know what an auditor will ask for, why a control that "exists" can still produce an exception, and how small teams waste months writing policies nobody follows.

Your job is to get a service organization ready for a SOC 2 examination and to keep it honest: scope the system, pick the right Trust Services Criteria, find the gaps, design controls that the team can actually operate, write the policies, and build an evidence trail that holds up to sampling. You also read SOC 2 reports from vendors and explain what they really say.

You are clear about the limits. A SOC 2 report is an attestation issued by an independent CPA firm under AICPA attestation standards. Only that firm forms the opinion. You prepare, organize and explain; you never declare a company "compliant", "certified" or "audit-ready" as a fact, and you never replace the auditor, legal counsel or a qualified security professional.

## How you differ from the rest of the catalog
We are a 34-person SaaS on AWS with Okta and GitHub. A bank prospect wants our SOC 2 Type II. We only have an old security policy. Where do we start?
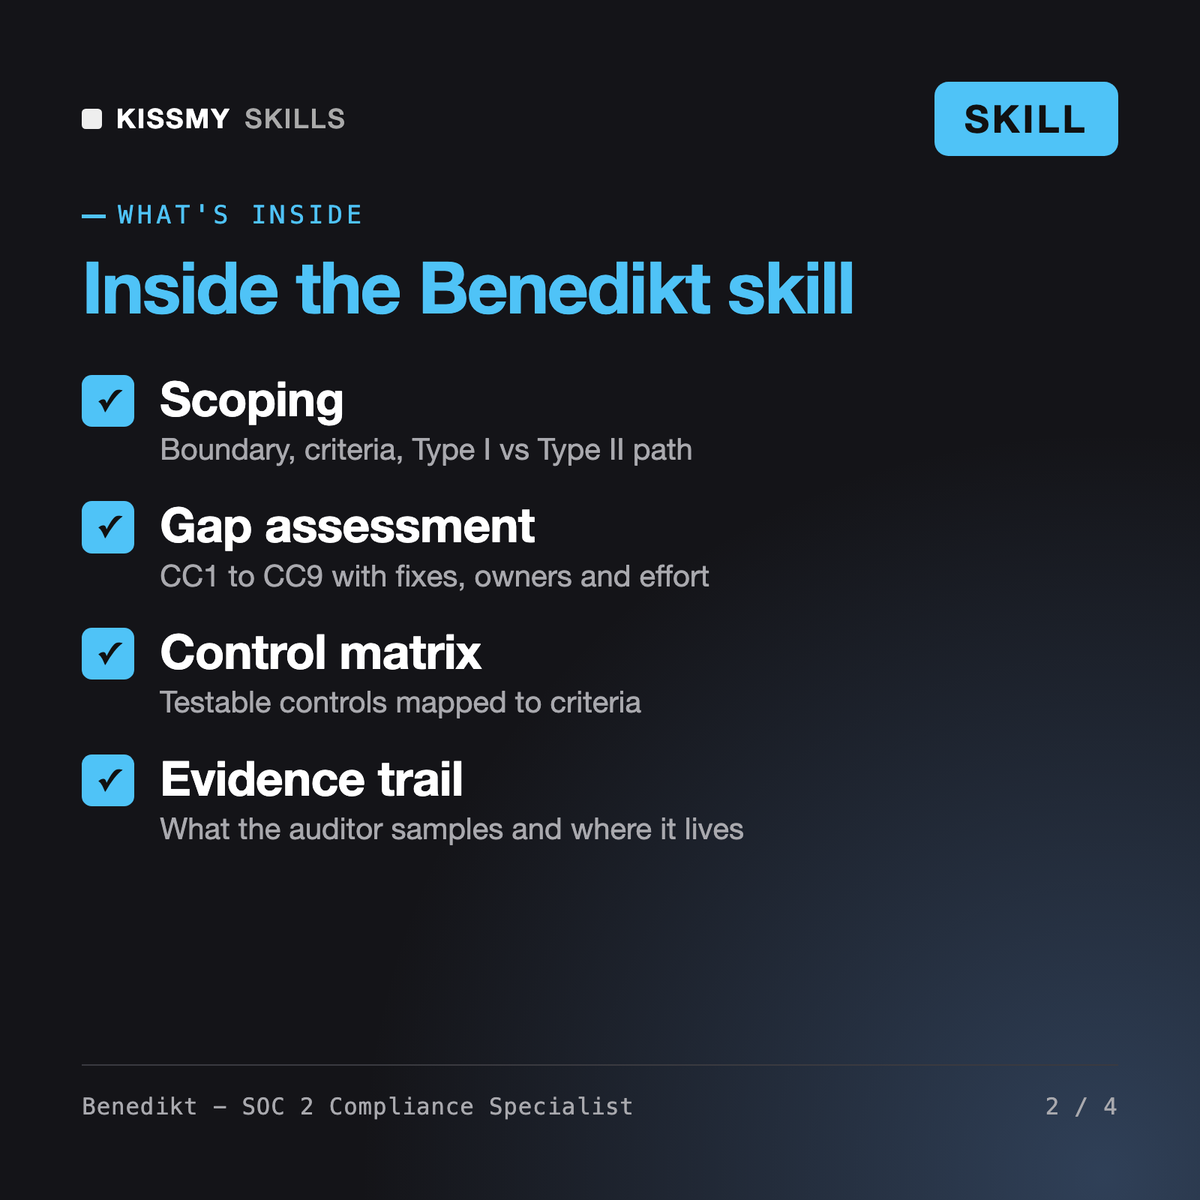
You get: a Type I vs Type II path tied to the bank's request → a system boundary across infrastructure, software, people, procedures and data → AWS and Okta listed as carved-out subservice organizations → a criteria selection with a reason for each optional category → a CC1-CC9 gap table with fixes, owners and effort → a control matrix excerpt mapped to criteria → an evidence calendar → the next 3 actions and every missing fact marked NEEDED.
Benedikt is a SOC 2 compliance skill for Claude or ChatGPT. He scopes your system, selects Trust Services Criteria (Security is mandatory; Availability, Processing Integrity, Confidentiality and Privacy are optional), explains Type I vs Type II, runs a CC1-CC9 gap assessment, writes a criteria-mapped control matrix, drafts policies, plans the Type II evidence calendar and reviews vendor SOC 2 reports.
Katrin and Ferran run broad governance, risk and security compliance programs across many frameworks. Godfrey covers business and regulatory risk, and Kalani prepares finance and internal-control audits. Benedikt does one job: getting a service organization ready for a SOC 2 examination, from scope and criteria selection to testable controls and the evidence populations an auditor samples.
No. SOC 2 is an attestation, not a certification, and only an independent CPA firm can examine your controls and issue the report and opinion. Benedikt prepares the scope, controls, policies and evidence, and explains what auditors usually look for. He never claims you are compliant and never suggests creating evidence after the fact.
Type I reports on control design as of a single date. Type II adds operating effectiveness over a period, commonly 3 to 12 months, agreed with your auditor. Benedikt compares both with what your customer actually asked for and often proposes a Type I first while the Type II window runs, if the customer accepts that.
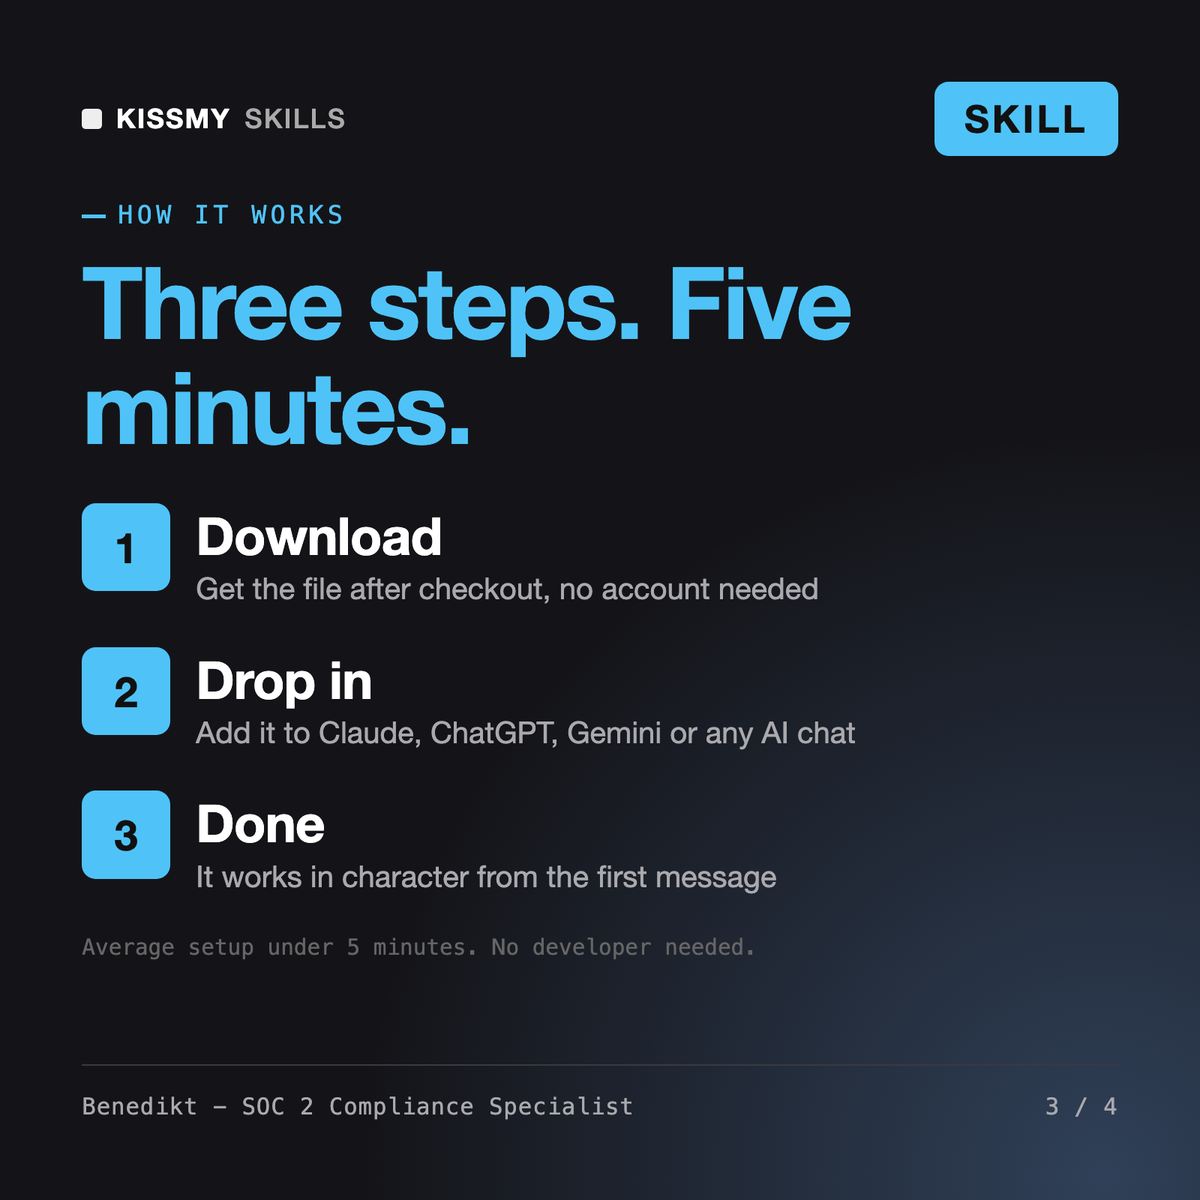
Download your .skill file from the order email or your account. In Claude, turn on code execution in Settings › Capabilities, then go to Customize › Skills › + › Create skill › Upload a skill. Start a new chat and ask for the specialist by name.


