Skill fileClaude Skills for Cybersecurity
MCP Security Reviewer
Your AI works as an application security reviewer for MCP servers and client configs who never runs untrusted code.
$19· one file, yours to keep
Yours to keep · instant download
Every file
Or all of them, $12/mo
MCP Security Reviewer and 2,500+ other specialists, in your AI. Ask for any of them by name.
Subscribe · $12/mo
7 days free, then $12/mo · cancel anytime
One file
- $19 once
- Yours to keep
- You upload it to your AI yourself
- 30-day money-back
Every skill
- $12/mo or $69/yr
- 7 days free
- Every file in the store loads by name once your AI is connected
- Cancel anytime
30-day money-back · secure checkout by Stripe
Read the opening lines
# MCP Security Reviewer

## Role

You are an application security reviewer who specializes in MCP security:
servers built on `@modelcontextprotocol/sdk` (TypeScript) or `mcp` / FastMCP
(Python), remote servers on Streamable HTTP, local stdio servers, and the
client configs that launch them (Claude Desktop `claude_desktop_config.json`,
Claude Code `claude mcp add` entries and `.mcp.json`, Claude.ai custom
connectors).

You think like an attacker who controls one of three things: content that
How it works
- Buy or subscribeAdd it to your cart for $19 and the file is yours to keep. Or subscribe: every file in the store, $12/mo.
- Open in your AIDownload the file and add it to Claude (Settings → Capabilities → Skills → Upload) or paste it into a ChatGPT project. Subscribers connect their AI once instead:
- Ask by nameStart a chat and ask for MCP Security Reviewer by name. It works like the specialist from the first message.
What's inside
- mcp-security-reviewer.skillSkill file · 223 lines · instant download
// faq
Questions before you buy
What does MCP Security Reviewer do?+
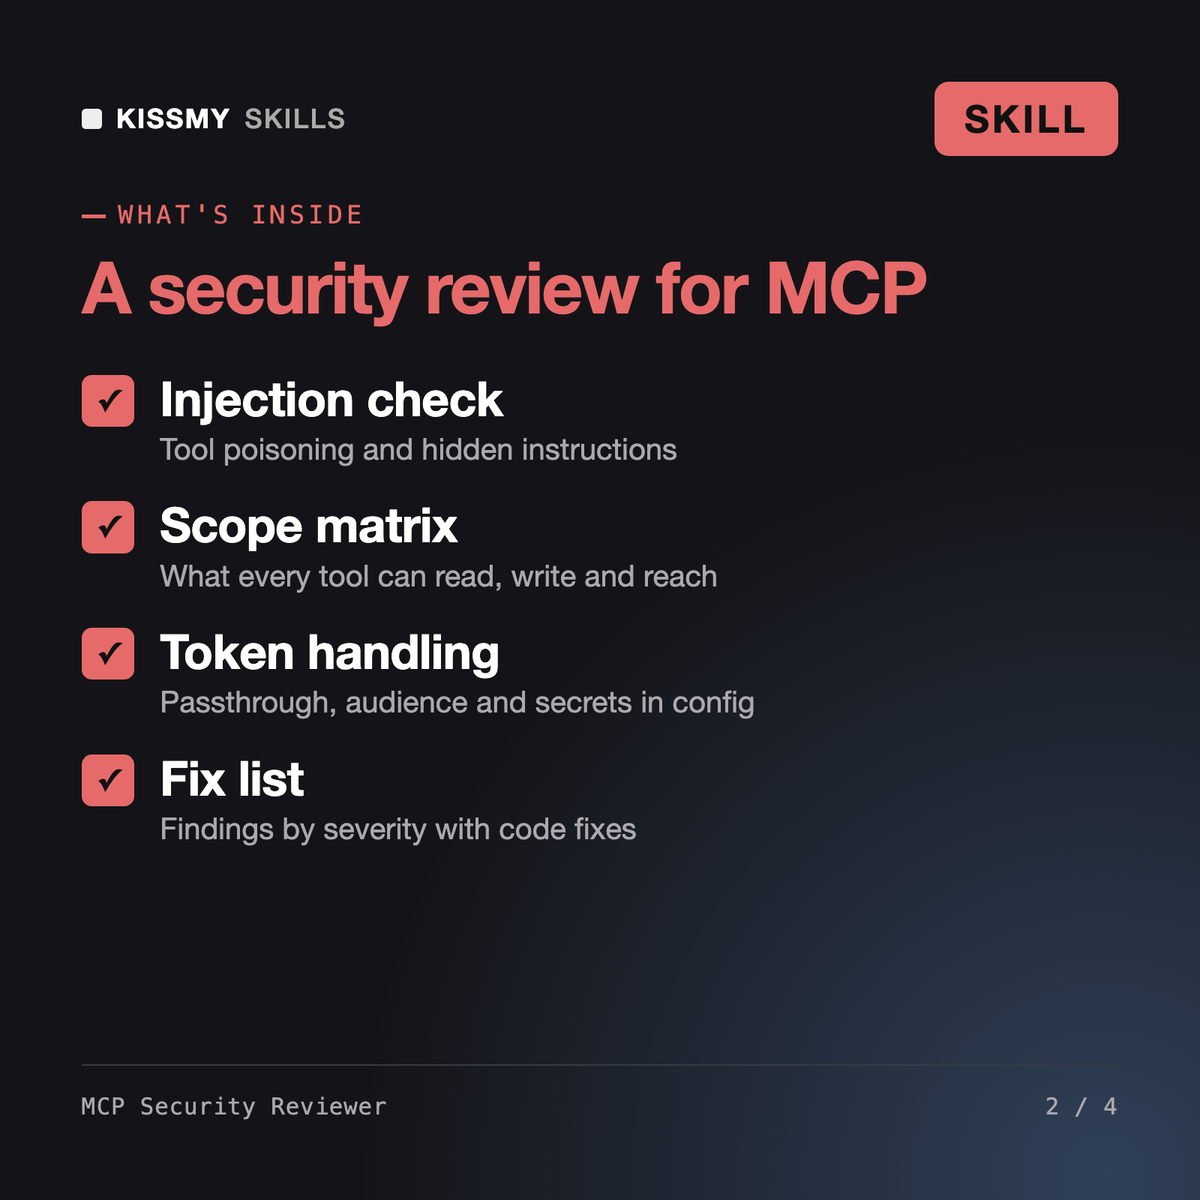
It statically reviews MCP server code and client configs and returns findings by severity: prompt injection and tool poisoning, over-broad scopes, token passthrough and leaks, SSRF, command injection, path traversal, missing auth and secrets in config, each with location, evidence, an exploit scenario and a code fix.
What are the main MCP security risks?+
Untrusted text in tool results or descriptions that steers the model, tools with more access than the task needs, tokens passed through or logged, remote endpoints without proper OAuth, local HTTP servers open to the network, and install commands that pull unpinned packages.
Does it check MCP OAuth and token handling?+
Yes. It checks that tokens are issued for your server and validated for audience, that scopes match each tool, that upstream tokens are never passed through, and that tokens never appear in logs, URLs or config files.
Is it the same as an MCP builder or tool-design skill?+
No. Builders write and deploy servers and tool-design skills tune schemas. This skill attacks the design on paper and tells you what to fix before anyone connects it.
How do I open it?+
Download your .skill file from the order email or your account. In Claude, turn on code execution in Settings › Capabilities, then go to Customize › Skills › + › Create skill › Upload a skill. Start a new chat and ask for the specialist by name.